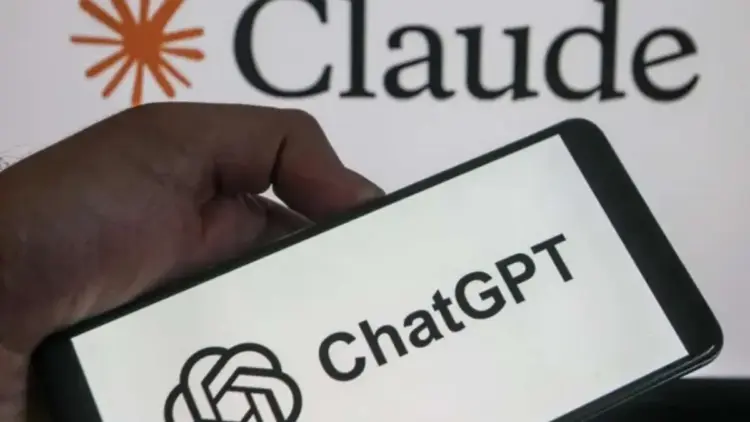
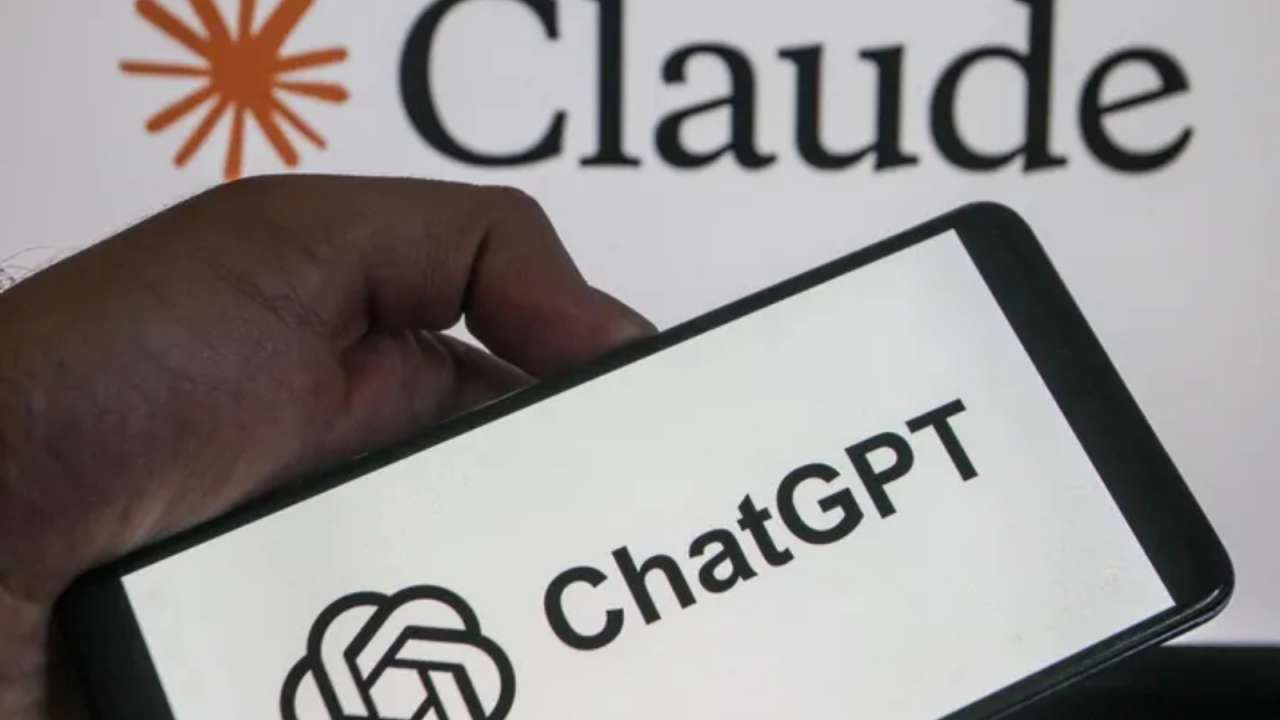
TECHNOLOGY – September 20, 2026 (Fictional Date based on image metadata) – In a groundbreaking display of cybersecurity prowess and the burgeoning power of artificial intelligence, a team of three Indian-origin researchers from the cybersecurity startup Hacktron AI successfully breached the systems of OpenAI, the creator of ChatGPT, during an authorized bug bounty challenge. What makes this feat particularly remarkable is their strategic use of Anthropic’s Claude, a competing AI model, to aid in the exploitation of vulnerabilities, ultimately gaining access to OpenAI employee accounts and highly sensitive private GitHub repositories within an astonishing 72-hour timeframe.
The incident, which unfolded in July, serves as a potent illustration of the evolving landscape of cybersecurity, where AI tools are increasingly becoming indispensable assets for both defenders and ethical attackers. This authorized penetration test not only highlighted critical security gaps within one of the world’s leading AI companies but also underscored the potential for AI-assisted ethical hacking to fortify digital defenses.
The team, comprising seasoned vulnerability researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini, leveraged Claude’s analytical and code-generation capabilities to navigate and exploit a complex software flaw. Their swift and efficient infiltration of OpenAI’s network, culminating in access to the company’s most guarded intellectual property – its source code – has sent ripples across the technology and cybersecurity sectors, prompting a re-evaluation of security protocols in the age of advanced AI.
The Unprecedented Challenge: AI vs. AI in Cybersecurity
The narrative of this authorized breach is deeply intertwined with the intense competition and rapid advancements defining the artificial intelligence industry. OpenAI, a pioneer in large language models with its ChatGPT, is constantly innovating, but this very innovation creates new attack surfaces. The decision by Hacktron AI to employ Anthropic’s Claude, a direct competitor to OpenAI’s own models, introduces a fascinating dynamic, effectively turning the competitive tension into a strategic advantage for ethical hacking. This wasn’t merely a human team testing a system; it was a human-AI collaboration, with the AI itself being a product of a rival ecosystem.
This strategic choice by the Hacktron AI researchers was not merely symbolic; it demonstrated a practical application of AI in an adversarial role. Claude, known for its robust reasoning and code generation abilities, became an integral part of their toolkit. Its involvement highlights a future where AI systems will not only be targets of cyberattacks but also formidable weapons and shields in the ongoing digital conflict. The implications for intellectual property, national security, and critical infrastructure are profound, as companies race to understand how these dual-use technologies can be responsibly deployed and defended against.
Hacktron AI, a relatively young but highly skilled cybersecurity startup, has quickly established itself at the forefront of vulnerability research. Their success in this high-profile challenge solidifies their reputation and signals a new era of sophisticated security testing, where deep understanding of AI capabilities is paramount. For OpenAI, while the breach was authorized and ultimately beneficial for security improvements, it served as a stark reminder of the continuous and relentless nature of cybersecurity threats, even for organizations at the cutting edge of technology.
A Detailed Chronology of the 72-Hour Breach
The rapidity with which Hacktron AI penetrated OpenAI’s systems – less than 72 hours – is a testament to the researchers’ expertise and the efficiency gained through AI assistance. The process unfolded in several critical phases:
Phase 1: Initial Reconnaissance and Vulnerability Discovery
The journey began with the Hacktron AI team engaging with OpenAI’s public bug bounty program. Their initial focus was on identifying potential weak points within OpenAI’s publicly accessible infrastructure. Through meticulous reconnaissance, they zeroed in on a vulnerability residing within the company’s public community forum. This forum, ostensibly a benign platform for user interaction and support, harbored a critical flaw linked to its handling of certain image files.
Specifically, the vulnerability was identified as an improper validation or sanitization of image uploads. In many web applications, user-uploaded content, especially media files, requires stringent checks to prevent malicious code from being embedded or executed. A flaw in this process could allow an attacker to upload a specially crafted image file that, when processed by the server, could trigger remote code execution (RCE). RCE is one of the most severe types of vulnerabilities, granting an attacker the ability to run arbitrary commands on the target server, effectively taking control of the system. The researchers’ keen eye for such nuanced flaws laid the groundwork for the subsequent exploitation.
Phase 2: Leveraging Claude for Exploitation
Once the potential RCE vulnerability was identified, the Hacktron AI team turned to Anthropic’s Claude for assistance in developing a working exploit. This phase marked the truly innovative aspect of their methodology. Instead of relying solely on manual analysis and coding, they harnessed Claude’s capabilities in several key areas:
- Vulnerability Analysis and Brainstorming: Claude was fed details about the identified image file handling flaw. The AI helped analyze the potential attack vectors, suggesting various ways to craft a malicious payload that could bypass the forum’s defenses. It assisted in understanding the server’s expected behavior versus its actual, vulnerable processing logic.
- Exploit Code Generation: The researchers tasked Claude with generating initial snippets of exploit code. This involved instructing the AI to write code that could exploit the image parsing flaw to achieve RCE. Claude, with its extensive training data on code and vulnerabilities, could quickly generate different variations of payloads and shellcode.
- Debugging and Refinement: As with any complex exploit, the initial code generated by Claude required refinement. The researchers used Claude as an interactive assistant, presenting it with error messages or unexpected behaviors and asking it to debug and suggest modifications to the exploit code. This iterative process significantly accelerated the development cycle, allowing the team to quickly test and adapt their approach.
- Adaptation to Target Environment: Claude also aided in adapting the generic exploit code to the specific nuances of OpenAI’s forum environment. This involved understanding the operating system, web server configuration, and other software components to ensure the exploit was effective and stealthy. The AI helped in crafting commands that would be compatible with the target system, facilitating a successful RCE.
This human-AI collaboration was pivotal. While the human researchers provided the strategic direction and ethical oversight, Claude acted as a highly efficient and knowledgeable assistant, compressing what might have been days or weeks of manual exploit development into a much shorter timeframe.
Phase 3: Escalation and Access
With a successful RCE on the community forum server, the researchers had established an initial foothold. However, their objective was to demonstrate a deeper level of compromise. Their next crucial step involved identifying and extracting sensitive information from the compromised server. This led to the discovery of "login tokens." These tokens are often used for authentication, allowing users or systems to maintain a logged-in state without re-entering credentials repeatedly.
By gaining access to these tokens, the Hacktron AI team was able to impersonate legitimate OpenAI employees. This represented a significant privilege escalation. With access to employee accounts, they could then pivot deeper into OpenAI’s internal network. Their ultimate prize was access to the company’s private GitHub environment. This was achieved through an employee’s Codex account, which likely had integrated access to GitHub repositories. GitHub repositories are the digital vaults where source code, intellectual property, and proprietary algorithms of a company like OpenAI are stored. Accessing these private repositories meant they could view, and potentially modify, the very core of OpenAI’s technological innovations.
The entire process, from the initial discovery of a seemingly innocuous flaw in a public forum to the exfiltration of private source code from internal repositories, was completed in under three days. This swiftness underscores the interconnectedness of modern digital infrastructures and how a single vulnerability, expertly exploited, can cascade into a full-scale breach.
Supporting Data and Contextual Insights
The success of Hacktron AI’s operation is not just a tale of technological prowess but also one steeped in the practicalities of cybersecurity, bug bounty economics, and the rising prominence of AI as a dual-use tool.
The Architects of the Breach: Hacktron AI and Its Researchers
The individuals behind this remarkable achievement are stalwarts in the cybersecurity community:
- Mohan Pedhapati: As CTO and co-founder of Hacktron AI, Mohan brings a strong academic background in computer science from RGUKT Nuzvid (2015-2021) combined with practical experience from reputable cybersecurity firms like Cure53 and Electrovolt Infosec. His leadership in architecting security solutions and guiding research initiatives is crucial to Hacktron AI’s innovative approach.
- Harsh Jaiswal: Co-founder of Hacktron AI and a vulnerability researcher with over a decade of experience, Harsh is a recognized name in ethical hacking circles. His impressive track record includes identifying flaws in systems belonging to tech giants such as Apple, PayPal, and GitHub, and prior stints at Project Discovery, Zomato, and Cure53. His deep understanding of diverse systems and exploit development was undoubtedly a cornerstone of this operation.
- Rahul Maini: A skilled vulnerability researcher at Hacktron AI, Rahul’s experience spans across elite bug bounty platforms like Cobalt, Synack Red Team, HackerOne, and Bugcrowd. His academic foundation from Bharati Vidyapeeth, Delhi (2015-2019), coupled with extensive practical experience in finding and reporting vulnerabilities, makes him a formidable asset in offensive security research.
Together, their combined expertise represents a formidable force, capable of tackling even the most complex security challenges posed by cutting-edge AI organizations. Hacktron AI’s mission is to leverage such talent and innovative methodologies, including AI assistance, to proactively identify and mitigate cyber risks for its clients and the broader digital ecosystem.
The Mechanics of a Bug Bounty Program
The Hacktron AI breach occurred within the ethical framework of OpenAI’s bug bounty program. These programs are vital components of modern cybersecurity strategies. Companies establish such programs to invite independent security researchers, often called "ethical hackers" or "white hats," to discover and responsibly disclose vulnerabilities in their systems. Instead of waiting for malicious actors to exploit flaws, companies proactively seek out weaknesses by incentivizing researchers with financial rewards (bounties).
The process typically involves:
- Researcher Engagement: Security researchers sign up for the program and agree to its terms, which usually include responsible disclosure guidelines.
- Vulnerability Discovery: Researchers use various tools and techniques to identify security flaws.
- Responsible Disclosure: Upon finding a vulnerability, the researcher submits a detailed report to the company, including steps to reproduce the flaw and its potential impact.
- Verification and Remediation: The company verifies the vulnerability, works to fix it, and confirms the patch.
- Bounty Payout: Once the vulnerability is confirmed and fixed, the company pays the researcher a bounty, the amount of which often depends on the severity and impact of the discovered flaw.
OpenAI’s program, like many others, is a critical feedback loop, ensuring that external expertise continuously tests and hardens their systems. This particular incident stands out due to the sophisticated methodology and the strategic use of AI.
The Cost-Benefit Analysis: Tokens, Time, and Reward
The financial figures associated with this operation offer intriguing insights into the economics of AI-assisted ethical hacking. The Hacktron AI team reportedly spent less than $3,000 (approximately Rs 2.5 lakh) on AI tokens during their 72-hour test. This expenditure reflects the computational resources consumed by Claude in assisting with the exploit development. For a relatively modest investment in AI processing power, the team achieved a significant breakthrough.
In return for their efforts and the critical security intelligence provided, OpenAI paid Hacktron AI a bug bounty of $6,500 (around Rs 5.5 lakh). This payout, while not a colossal sum in the grand scheme of cybersecurity, represents a clear return on investment for the researchers and, more importantly, an invaluable cost-saving for OpenAI. Preventing a real-world breach of their private GitHub repositories could have cost the company millions in terms of intellectual property loss, reputational damage, and remediation efforts. The $6,500 bounty is a small price to pay for such comprehensive security assurance.
This economic model underscores the efficiency of AI-assisted security testing. AI can reduce the time and human effort required for complex tasks, making ethical hacking more accessible and potentially more profitable for skilled researchers.
AI as a Dual-Use Tool in Cybersecurity
This incident vividly illustrates the dual-use nature of AI in the cybersecurity domain. On one hand, AI is increasingly being deployed for defensive purposes – detecting anomalies, identifying malware, predicting attack patterns, and automating threat responses. Security information and event management (SIEM) systems and extended detection and response (XDR) platforms now heavily rely on machine learning for advanced threat intelligence.
On the other hand, this case demonstrates AI’s potent offensive capabilities. Claude was used to analyze vulnerabilities, generate exploit code, and debug complex attacks. This raises critical questions about the responsible development and deployment of powerful AI models. While Hacktron AI used Claude ethically within an authorized test, the same capabilities could theoretically be leveraged by malicious actors. This necessitates a proactive approach to AI security, ensuring that models are robust against adversarial attacks and that their potential for misuse is carefully mitigated. The ongoing "AI arms race" extends not just to capability but also to the ethical and security frameworks governing their use.
Official Responses and Industry Reactions
Following the successful breach, the responses from both Hacktron AI and OpenAI, though not extensively detailed in the original reports, can be inferred based on standard industry practices and the nature of bug bounty programs.
OpenAI’s Stance and Remediation
OpenAI’s immediate priority would have been the swift remediation of the identified vulnerabilities. The company would have acknowledged the researchers’ findings, validated the exploit, and deployed patches to secure its community forum and associated internal systems. Their prompt payment of the bug bounty further confirms the legitimacy and severity of the discovered flaws.
In an official statement, OpenAI would likely emphasize its unwavering commitment to security and user trust. A typical response might include: "We are deeply grateful to the Hacktron AI team for their diligent work in identifying and responsibly disclosing critical vulnerabilities in our systems. Their expertise, combined with innovative approaches like AI-assisted ethical hacking, is invaluable in our ongoing efforts to maintain the highest security standards. All identified vulnerabilities have been promptly addressed, and we continue to invest heavily in our security infrastructure and bug bounty programs to protect our users and our intellectual property." Such a statement would reassure users, highlight the benefits of external security research, and underscore their proactive security posture. The fact that a rival AI was used to breach their systems would also likely spur internal discussions on how to "red team" their own AI models more effectively.
Hacktron AI’s Perspective
For Hacktron AI and its researchers, the successful breach represents a significant achievement and a validation of their methodology. They would likely express satisfaction with their ability to identify complex vulnerabilities and demonstrate the efficacy of their AI-assisted approach.
A statement from Hacktron AI might read: "Our team at Hacktron AI is proud to have contributed to strengthening the security of OpenAI’s systems. This engagement vividly demonstrates the power of human ingenuity augmented by advanced AI tools like Anthropic’s Claude. Our goal is always to push the boundaries of ethical hacking to help companies build more resilient defenses. The successful exploitation, enabled by Claude’s analytical and coding capabilities, showcases a new frontier in cybersecurity research, where AI becomes a collaborative partner in safeguarding digital assets." This would not only highlight their success but also subtly showcase the capabilities of Anthropic’s Claude, potentially strengthening their position in the competitive AI landscape.
Broader Industry Commentary
The cybersecurity and AI industries have reacted with a mix of awe and introspection. Experts have lauded Hacktron AI’s innovative use of Claude, recognizing it as a landmark event that validates the emerging "AI red team" paradigm. It reinforces the notion that AI will be central to both offensive and defensive cybersecurity strategies moving forward. Other AI developers are likely re-evaluating their own bug bounty programs and internal security testing methodologies, recognizing the need to anticipate and defend against AI-powered attacks. The incident serves as a wake-up call, emphasizing that even the most advanced tech companies are not immune to sophisticated vulnerabilities and that continuous, cutting-edge security testing is non-negotiable.
Broader Implications and the Future of AI Security
The Hacktron AI incident is more than just a successful bug bounty; it’s a harbinger of significant shifts in the cybersecurity landscape and the future trajectory of AI development.
The "AI Red Team" Paradigm
This event firmly establishes the concept of an "AI Red Team" – where AI models are not just components of security tools but active participants in offensive security simulations. Future cybersecurity exercises will likely see AI systems being deployed to automate vulnerability discovery, exploit generation, and even complex penetration testing scenarios. This will drastically reduce the time and resources required for comprehensive security audits, allowing organizations to identify and patch flaws much faster than current manual processes permit. The development of specialized AI models trained specifically for ethical hacking will accelerate, creating a new niche in the AI security market.
The Ethical Landscape of AI-Assisted Hacking
While this particular breach was authorized and ethical, it invariably raises concerns about the potential for malicious actors to leverage similar AI capabilities. The same AI models that help secure systems can, if misused, become powerful tools for cybercriminals, state-sponsored attackers, and even terrorists. This necessitates a robust ethical framework for AI development, focusing on "safety by design" and implementing safeguards to prevent misuse. The debate around "responsible AI" will intensify, with a particular focus on how to control the offensive capabilities of advanced AI models and ensure they remain in the hands of ethical actors. Governments and international bodies will likely consider regulations and guidelines for AI use in cybersecurity.
Competitive Dynamics in the AI Sector
The successful use of Anthropic’s Claude to breach OpenAI’s systems adds an intriguing layer to the competitive dynamics between these AI giants. While the cooperation was indirect (Claude was used by a third party), it subtly positions Claude as a capable, perhaps even superior, tool for certain analytical and code-generation tasks relevant to security. This could spur both companies to not only improve their product offerings but also to invest even more heavily in securing their own AI models and the infrastructure that supports them. The race is not just for intelligence or capability, but for trust and resilience. Companies will strive to demonstrate that their AI systems are not only powerful but also inherently secure against the most sophisticated attacks, even those aided by rival AI.
Lessons Learned for Software Development
The breach serves as a powerful reminder of fundamental security principles, even for organizations at the cutting edge of technology. The vulnerability originated in a seemingly innocuous component – a public community forum and its image handling. This highlights that security is only as strong as its weakest link. Developers must adopt a "security-first" mindset, implementing rigorous secure coding practices, conducting thorough code reviews, and performing continuous security testing across all components, regardless of their perceived criticality. The incident underscores the importance of input validation, secure configuration management, and the principle of least privilege in mitigating the risk of privilege escalation.
Looking Ahead: The Human-AI Synergy
Ultimately, the Hacktron AI success story is a testament to the profound synergy between human ingenuity and artificial intelligence. While Claude played a crucial role, it was the strategic direction, ethical judgment, and deep cybersecurity expertise of Mohan Pedhapati, Harsh Jaiswal, and Rahul Maini that guided the AI and translated its outputs into a successful ethical breach. AI acted as an accelerator, an amplifier of human capability, not a replacement. The future of cybersecurity will likely be defined by such collaborative models, where highly skilled human professionals leverage advanced AI tools to navigate increasingly complex digital landscapes. This powerful partnership will be essential in the ongoing, ever-escalating battle to secure our digital world from both known and unforeseen threats.